London | Austin | Dubai · One international team · One delivery standard
Technology decisions carry business-wide consequences
We help organisations address the risks, governance challenges and implementation demands created by cyber security, technology change and responsible AI adoption.
Explore this priorityThree connected practices. One standard of delivery.
Cyber Security, Technology Risk & GRC, and AI Governance are connected disciplines. Captavio brings them together to reduce risk, strengthen governance and build capability that works in practice.
Explore the practice
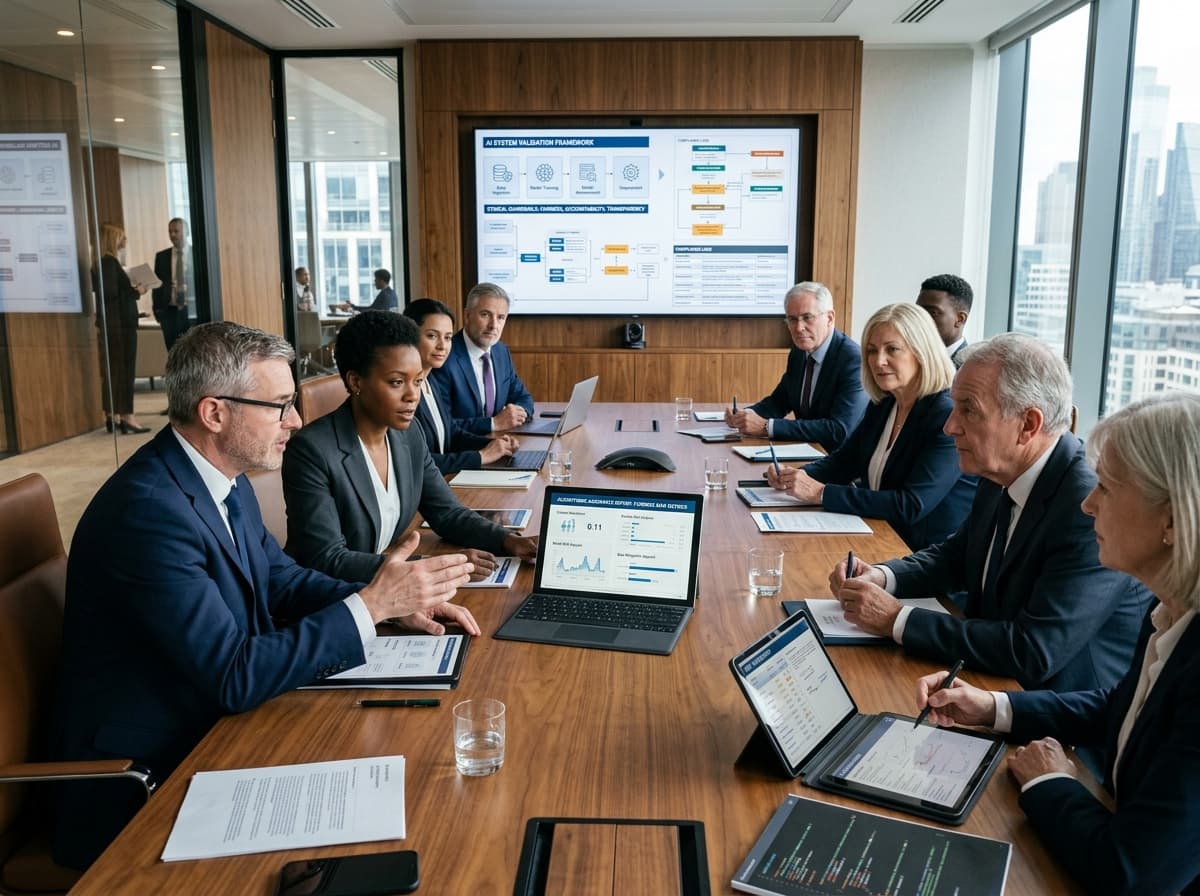
From Assessment to Assurance
Most organisations already have assessments, reports and recommendations. The real challenge is turning them into working capabilities, measurable improvements and lasting assurance. Captavio supports implementation, improvement and independent review so leadership can have confidence in the outcome.
See how we deliverThe Captavio Digital Trust Model
Digital Trust is confidence in the technology, governance and digital decisions the organisation depends on.
Cyber Security, Technology Risk & GRC, and AI Governance work together to create this confidence. Implemented capability and assurance provide the foundation.
Security
Risk & GRC
Trust
Governance
Confidence outcomes delivered to leadership
Why organisations partner with Captavio
Experienced Practitioners
Senior advisers with deep technical, governance and regulatory experience leading every engagement.
Practical Delivery
We turn recommendations and strategies into working capabilities that your organisation can operate and own.
International Coverage
Seamless advisory delivery across London, Austin and Dubai under one unified team.
One Consistent Standard
Consistent methodology, high-calibre execution and rigorous assurance across all jurisdictions.
Certifications, standards and professional credentials
Our advisory delivery is grounded in recognised international standards, formal accreditation baselines and certified practitioner qualifications.
Company Accreditations & Standards Alignment
Practitioner Delivery Qualifications
Evidence of delivery across complex environments
Explore verified case outcomes demonstrating how organisations have moved from initial risk discovery to implemented, audit-ready capability.
Explore client outcomesExperience Across Complex Environments
Every operating environment carries distinct risks, obligations and governance demands. We tailor our delivery to address the core challenges in each sector.


How we deliver lasting capability
A structured, transparent approach that moves the organisation from understanding the challenge to sustained improvement.
Explore how we deliverPractical improvements. Lasting results.
Selected examples of how organisations have moved beyond recommendations to implemented capability, stronger governance and reliable assurance.
Assurance Readiness & Control Visibility
Fragmented controls and lack of audit-ready evidence for institutional stakeholders.
Assessed control baselines, designed an operational risk framework, and implemented verifiable reporting.
Clear control visibility, prioritised remediation path, and robust ongoing assurance.
Security & Governance Maturity
Evolving cyber threats and increasing client compliance demands without clear maturity targets.
Conducted maturity assessments, established clear control ownership, and embedded operational response practices.
Documented maturity baseline, resolved priority gaps, and established continuous governance.
Responsible AI Governance & Oversight
Rapid adoption of predictive and generative AI tools without systematic risk oversight or regulatory alignment.
Built an AI inventory, classified high-risk use cases, and established board-level governance and lifecycle controls.
Defensible AI governance framework, model accountability, and compliance alignment.
